Application Security Testing Program: How to Build One That Survives Real Release Velocity
Key Highlights:
- Security testing programs collapse in practice when they slow releases down enough that fast-shipping SaaS and FinTech teams start finding ways around them.
- An application security testing program built around cadence and clear ownership survives contact with real release schedules.
- Getting this right reduces both vulnerability exposure and the friction between security and engineering teams, without slowing the release cadence investors and customers expect.
- Sigma builds security testing into the delivery pipeline itself for SaaS and FinTech clients, rather than treating it as a separate gate applied afterward.
Introduction
Most application security testing programs are designed once, in a planning document, and then quietly eroded over the following year as engineering teams find ways around a process that keeps slowing their releases down. This tension is sharpest at growth-stage SaaS and FinTech companies, which ship frequently to keep pace with competitors and investor expectations while also carrying compliance obligations, SOC 2 audits, PCI requirements, or financial regulatory review, that a slower, more established company might not face as directly. An application security testing program that actually holds up needs to be designed around the release cadence it will run alongside, not against it, with clear ownership for who triages findings and clear rules for what blocks a release versus what gets logged and scheduled. Getting that structure right the first time avoids the slow erosion that turns a well-intentioned program into a checkbox nobody actually enforces after the first few quarters.
Deciding Between In-House and Outsourced Testing Capacity
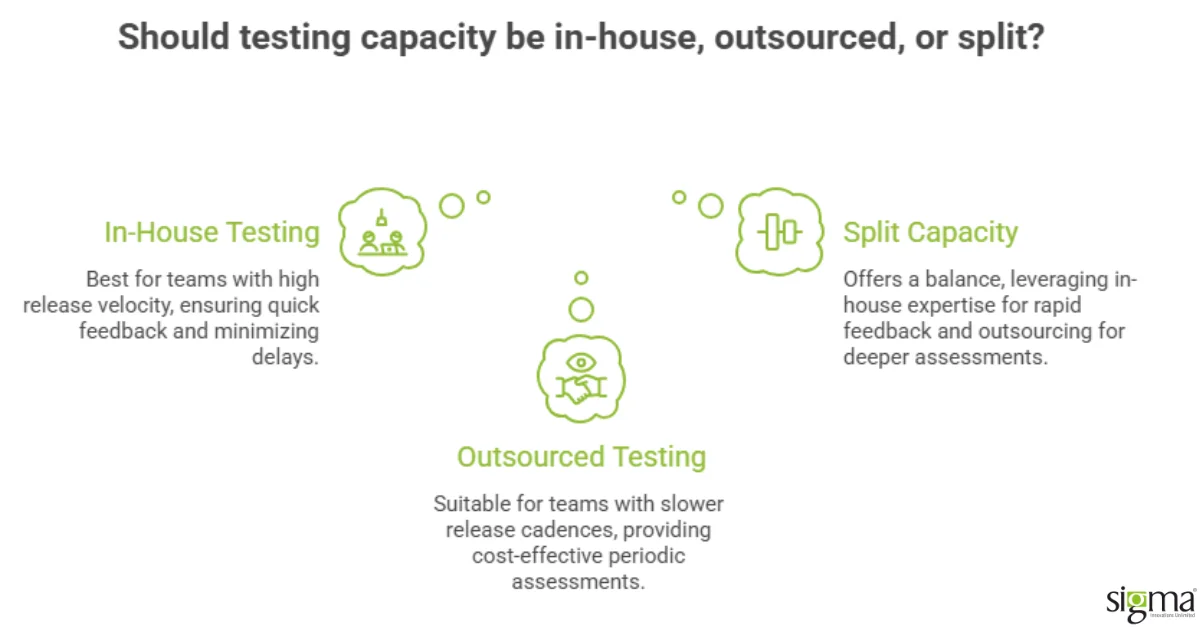
The first structural decision is whether testing capacity lives in-house, is outsourced to a specialist partner, or splits across both, and this decision should follow the team’s actual release velocity rather than a general preference. Teams shipping multiple releases per week need testing integrated tightly enough into continuous integration that findings surface before a merge completes, which usually favors in-house capacity that understands the codebase deeply and can tune out false positives quickly without a handoff delay. Teams with a slower, more predictable release cadence can often rely more heavily on a specialist partner running periodic deeper assessments, since the cost of a short turnaround delay matters less when releases are already spaced further apart.
Setting a Cadence for an Application Security Testing Program That Matches Risk, Not Just a Calendar
A common mistake is setting testing cadence by calendar convention, a quarterly penetration test regardless of how much the application has changed, rather than by actual risk exposure. An application handling payment data that ships weekly changes needs continuous automated scanning plus more frequent manual review than an internal tool that changes twice a year, yet many organizations apply the same quarterly cadence to both because it is easier to schedule uniformly. Tying cadence to a combination of release frequency and data sensitivity produces a program that actually matches where the risk lives, rather than one that looks consistent on a compliance calendar but leaves the highest-risk applications under-tested.
Also, read the blog : Build Smarter: The Ultimate C-Suite App Development Checklist
Comparing Cadence Models by Application Risk Tier
| Application Tier | Automated Scanning | Manual Review Cadence |
|---|---|---|
| High-risk, frequent releases | Continuous, gated in CI/CD | Quarterly, plus after major changes |
| Moderate-risk, regular releases | Continuous, gated in CI/CD | Semiannual |
| Low-risk, infrequent releases | Scheduled weekly or biweekly | Annual |
Defining Who Owns Triage and What Actually Blocks a Release
A testing program without clear ownership of triage produces findings nobody acts on, since a scan result sitting in a dashboard with no assigned owner is functionally the same as no scan at all. Effective programs assign triage ownership explicitly, typically a security engineer or a designated engineering lead, and define in advance which severity levels block a release versus which get logged and scheduled into a normal sprint. Without that distinction, teams either block every release over minor findings, which trains engineers to resent the process, or ignore everything because nothing is ever actually enforced, both of which defeat the purpose of running the program at all.
The same triage discipline that made that transformation work, clear ownership and a defined severity threshold, applies directly to structuring a security testing program that engineering teams actually respect rather than route around.
Integrating Testing Into CI/CD Without Becoming a Bottleneck
The technical integration matters as much as the organizational structure. Gating a merge on a full DAST scan that takes twenty minutes will eventually get bypassed under release pressure, while a fast SAST and SCA check that completes in under two minutes as part of the existing build pipeline tends to survive because it does not create a meaningful delay. Slower, deeper testing, DAST against staging or manual penetration testing, belongs on a separate cadence that runs alongside releases rather than blocking each one individually, which keeps release velocity intact while still covering the vulnerability classes that only surface at runtime.
The Release-Integrated Testing Program Sigma Builds for Development Organizations
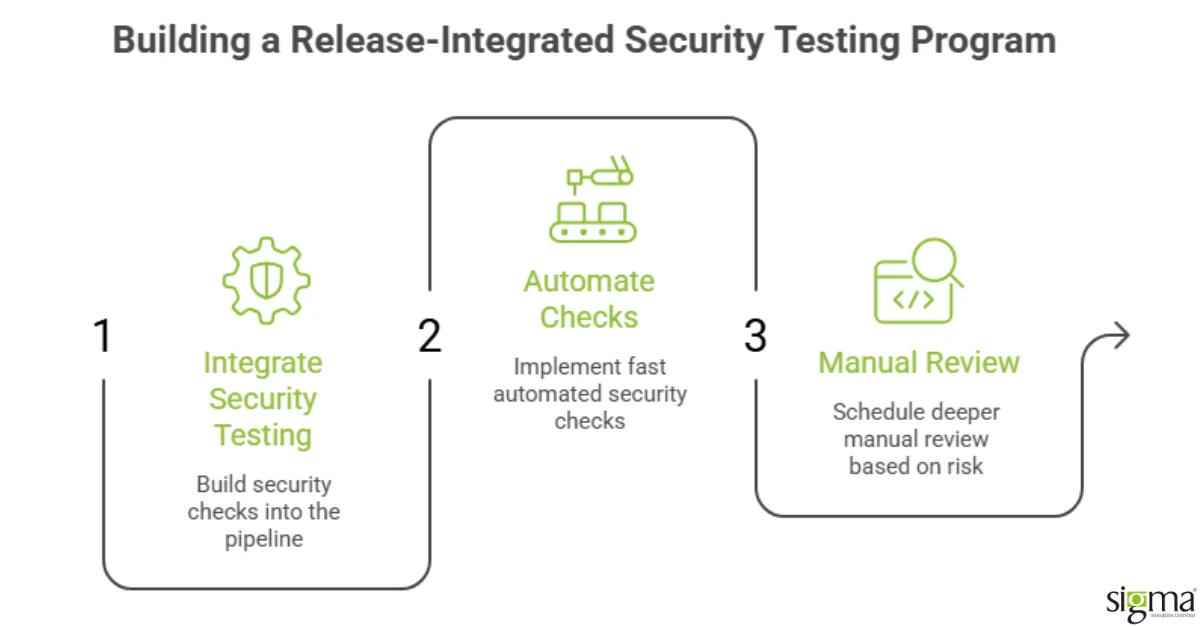
Sigma Infosolutions builds security testing into the delivery pipeline for the growth-stage SaaS and FinTech applications it maintains, using fast automated checks gated in continuous integration alongside a scheduled cadence of deeper manual review tied to each application’s actual risk tier. That approach draws on the same discipline applied to AI-assisted quality assurance work, where cutting cycle time and improving defect detection required rethinking where in the pipeline each type of check actually belonged, not simply adding more tools to an existing process.
Choosing the underlying tool categories, SAST, DAST, IAST, and SCA, is the other half of this decision and is covered in more depth separately, since tool selection and program structure need to be designed together rather than as sequential, disconnected decisions.
Handling Findings That Surface After a Release Has Already Shipped
Even a well-structured program will occasionally surface a finding after code has already reached production, whether from a delayed manual review or a newly disclosed vulnerability in a dependency that was considered safe last month. Treating this as a program failure misses the point; a mature program plans for it explicitly, with a defined incident response path that is distinct from the routine triage workflow used for pre-release findings. That path typically includes a faster severity assessment, a decision on whether to patch forward or roll back, and a retrospective step that asks whether the pre-release testing cadence should have caught the issue earlier. Programs that skip this step tend to repeat the same category of post-release finding, since nothing in the process actually changes after the first incident occurs.
Measuring Whether the Program Is Actually Working
Most teams measure a security testing program by counting findings, which is a weak signal, since a rising finding count can mean either a genuinely riskier codebase or simply better detection catching issues that were always there. A more useful set of metrics tracks time from finding to remediation, the percentage of findings that recur after being marked resolved, and whether critical findings are trending toward earlier detection in the pipeline over successive quarters. A program improving on these dimensions is functioning as intended, regardless of whether the raw finding count goes up or down in any given period.
For engineering directors, heads of engineering, and technology leaders responsible for software delivery, the executive-level consequence of a security testing program that does not survive release velocity is a compliance gap disguised as a program. Findings sit unaddressed in a dashboard, release friction builds, and the program either gets abandoned or reduced to a checkbox that no longer represents real coverage. The business risk that was meant to be managed is still present, and the investment in tooling and process produced neither coverage nor speed. The trade-off in designing a program around actual release cadence and risk tier is that it requires a more careful initial design than a standard quarterly penetration test schedule. That design investment, pairing fast automated gates in CI with slower periodic deep testing on a separate schedule, consistently produces a program that engineering teams actually run rather than route around. A program built this way reduces real exposure rather than generating a report that satisfies an audit requirement while leaving the codebase unexamined between scheduled reviews.
Sigma Infosolutions designs application security testing programs structured around the release cadence and risk profile of the specific engineering organization, rather than applying a standard template regardless of context. If your team needs a security testing program that runs alongside your actual release velocity rather than against it, speak with Sigma’s application security practice to scope the program design.
A security testing program that is not designed around actual release velocity creates a direct trade-off: either testing becomes a bottleneck that engineering routes around, or coverage gets skipped to protect the release date. Neither outcome is acceptable, which is why the program’s cadence needs to be built around the engineering team’s real deployment frequency rather than a standard imposed from outside it.
However, there is a real constraint on how far testing cadence can compress before it becomes the limitation that slows releases down, and that ceiling is a consideration engineering leadership should set deliberately rather than discover under deadline pressure.
Conclusion
An effective application security testing program is designed around the release cadence it runs alongside, not against it, with explicit ownership for triage and a clear, predefined severity threshold for what actually blocks a release. Programs designed once in a planning document and left unmaintained tend to erode as engineering teams find ways around a process that keeps slowing their releases down without a clear rationale attached to each check. Cadence should follow the risk tier, matching testing frequency to how often an application changes and how sensitive the data it handles actually is, rather than applying a uniform quarterly schedule regardless of exposure. Fast automated checks, SAST and SCA, belong directly in continuous integration where they complete quickly enough not to create release friction. Slower, deeper testing, DAST against staging and manual penetration testing, belongs on a separate schedule that runs alongside releases instead of blocking each one individually. Clear triage ownership prevents findings from sitting unaddressed in a dashboard, which is functionally equivalent to running no testing program at all. The choice between in-house and outsourced testing capacity should follow actual release velocity rather than a general staffing preference. Programs built this way tend to survive contact with real release pressure, since they were designed around it from the start rather than imposed on top of an existing workflow. Tool selection and program structure need to be designed together, since the right cadence depends partly on which categories of tools are already integrated into the pipeline. Getting the structure right the first time avoids the slow erosion that turns a well-intentioned security program into a checkbox nobody actually enforces after the first few quarters pass. Engineering leaders who treat testing cadence as a risk-based design decision, rather than a compliance calendar entry, end up with programs that actually reduce exposure.
Build Security Into Every Release
Align security testing with your release cadence and risk profile. Talk to Sigma
Frequently Asked Questions
Q: How often should an application security testing program run manual penetration tests?
Cadence should follow risk tier rather than a fixed calendar. High-risk applications handling sensitive data with frequent releases warrant quarterly manual review plus testing after major changes, while lower-risk, infrequently updated applications can reasonably run on an annual manual review cycle instead, without meaningfully increasing exposure.
Q: Should security testing be owned by engineering or a dedicated security team?
Either can work, but ownership needs to be explicit either way it is structured within the organization. What fails consistently is diffuse ownership, where findings appear in a dashboard with no assigned triage owner and no defined severity threshold for what actually blocks a release from shipping.
Q: How do we prevent security testing from slowing down our release velocity?
Keep fast checks, SAST and SCA, gated directly in continuous integration where they complete in minutes, and move slower checks like DAST and manual penetration testing onto a separate cadence that runs alongside releases rather than blocking each individual release every single time it ships.
Q: What severity level should actually block a release from shipping?
This should be defined explicitly in advance, not decided case by case under release pressure late in a busy weekly sprint cycle. Most effective programs block on critical and high-severity findings only, logging medium and low findings into a normal sprint backlog so the process does not train engineers to resent it.
Q: Can a small engineering team run an effective security testing program without dedicated security staff?
Yes, particularly by combining automated CI/CD-gated scanning with a specialist partner for periodic deeper manual review work on a defined schedule. This split gives continuous baseline coverage without requiring a full-time security hire, while still covering the vulnerability classes that automated tools alone cannot reliably catch.